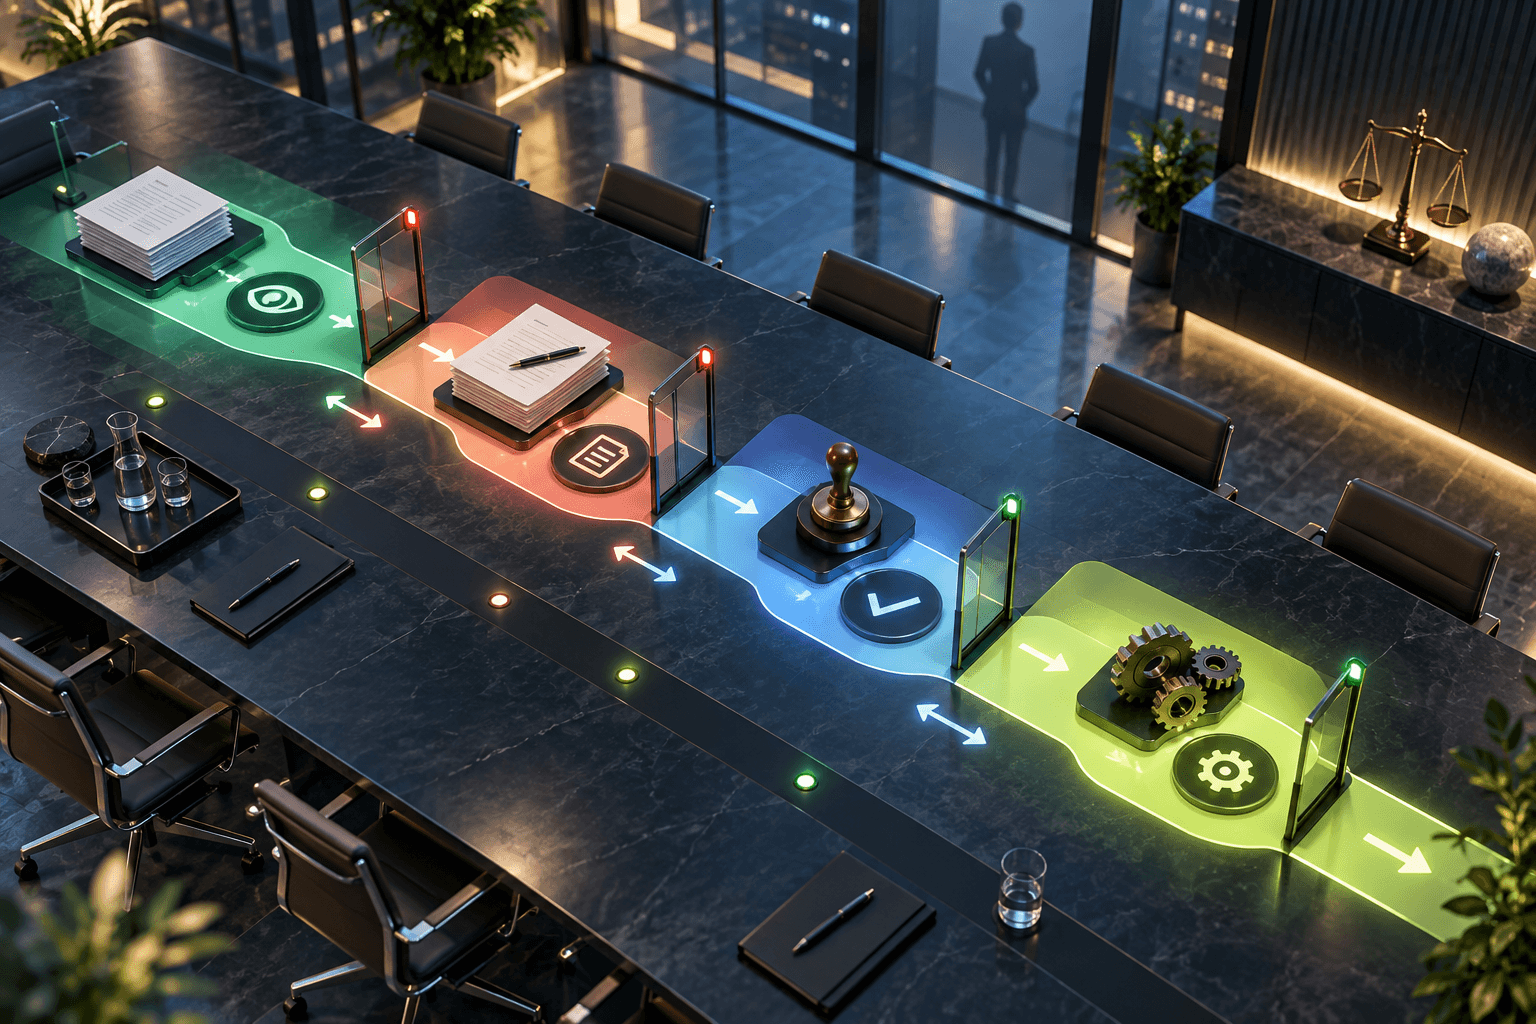
“Fully autonomous” is an easy product slogan but a poor default safety policy. Organizing notes and sending email are different risks, as are drafting and publishing. A mature agent automates low-risk steps and routes irreversible impact to an accountable reviewer.
1. The short answer
Risk comes from impact, reversibility, data sensitivity and legal consequence, not from whether a model sounds smart. A strong benchmark score does not remove new risk created by a new tool. Approval boundaries belong in server policy, not only in prompts.
2. The context
Use four tiers: public read, internal read, low-risk write and high-risk write. Automate and log the first two; preview, undo and limit low-risk writes; require itemized confirmation for high-risk writes with objects, fields, sources, reasons and impact.
3. The real trade-offs
An approval screen is not just approve or reject. It must show what the agent will do, which evidence it used, which fields will change and how failure can be reversed. For batch actions, show samples and totals and allow partial approval.
4. How to put it into practice
Measure approval waiting time, rejection, edit, rollback and post-approval failure. If humans rewrite every output, the automation boundary is wrong. If every approval is an instant click, the preview may not expose enough risk.
5. Common failure modes
Treating approval as an embarrassing patch leads to unreadable model output and incomplete context review. Place approval near the external side effect and preserve the full input-to-execution record.
6. FDE perspective
Automation should not eliminate every human decision. It should move human attention to the moments where consequences are high, while low-risk steps optimize for speed and high-risk steps optimize for explanation, reversibility and accountability.
A practical checklist before shipping or buying
- Tier actions by impact, reversibility, sensitivity and legal consequence.
- Show objects, sources, changed fields and impact for high-risk actions.
- Support partial approval, undo and complete audit trails.
- Track edits and failures after approval.
What to do next
Pick one existing workflow, separate drafting from execution, and expand permissions gradually.
This article is based on public documentation and research from NIST AI Risk Management Framework. The FDE perspective is editorial analysis, not a quotation from the source.
Turn this read into a practical next step.
Matched to this article automatically; each tool is managed independently from the admin.